SYSADMIN / ISSUE 01
Data Recovery,
Demystified.
An independent engineering journal dedicated to catastrophic outage recovery, storage forensics, and immutable backup systems. We maintain a strict zero-vendor editorial mandate: no sponsored hardware praise, no affiliate licensing bias, and no vendor interference.
Peer-reviewed technical whitepapers · 100% independent · Zero sponsorship
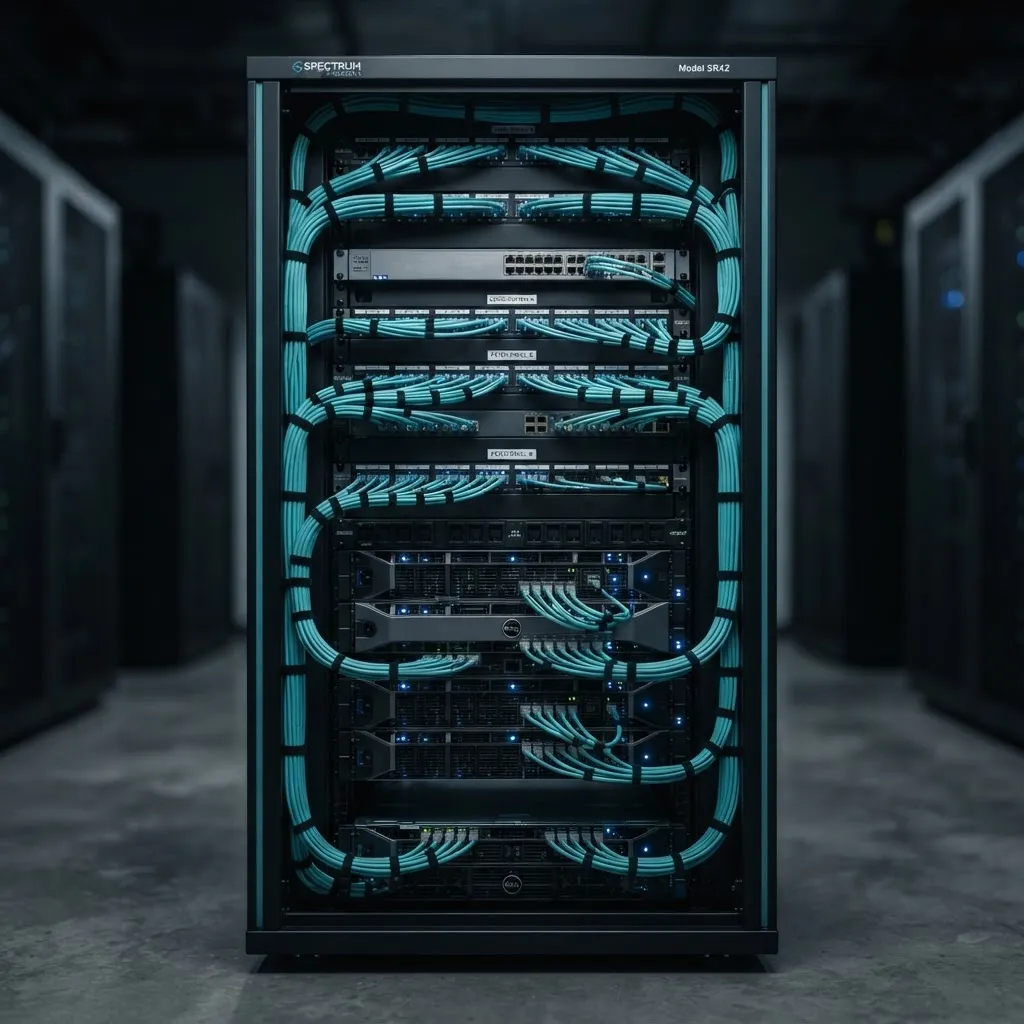
FIG 1.1: ISOLATED SAN ARRAY / AIR-GAPPED STORAGE VAULT
TECHNICAL RUNBOOKS & ARCHITECTURES
Essential Recovery Guides
Peer-reviewed recovery procedures, failover runbooks, and zero-trust snapshot architectures categorized by production environment and disaster tier.
Bare-Metal System State Recovery with ZFS & Btrfs Trees
Sub-minute local snapshot rollbacks, immutable send/receive streams, and zero-data-loss kernel panic isolation runbooks.
S3 Object Lock & Immutable Cloud Tiering for Ransomware
Hardening hybrid offsite repositories against root credential compromise via bucket governance policies and compliance retention.
Active Directory Forest Restoration & VSS Shadow Volume Sync
Tombstone object reanimation, authoritative SYSVOL repair sequences, and cross-datacenter hypervisor VSS snapshot recovery.
DISPATCHES & FIELD NOTES
Latest Analysis
Rigorous post-mortems, architecture reviews, and operational methodologies published without industry bias.
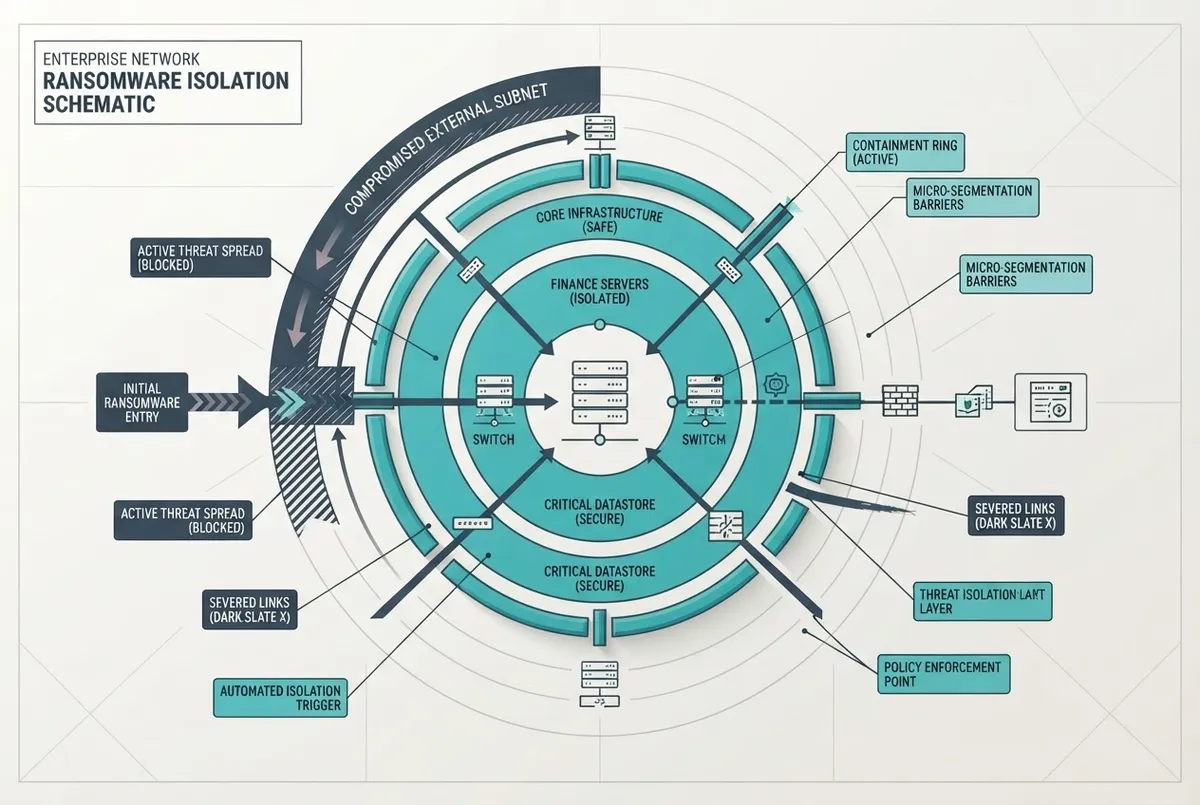
[SEC-092] · NOV 12, 2026 · ARCHITECTURE DEEP-DIVE
Ransomware Mitigation: Air-Gap Verification Protocols
Software-defined immutable vaults fail when hypervisor credentials leak. We test forensic methodologies for enforcing physical network segregation and cryptographic snapshot validation before encryption payloads initiate.
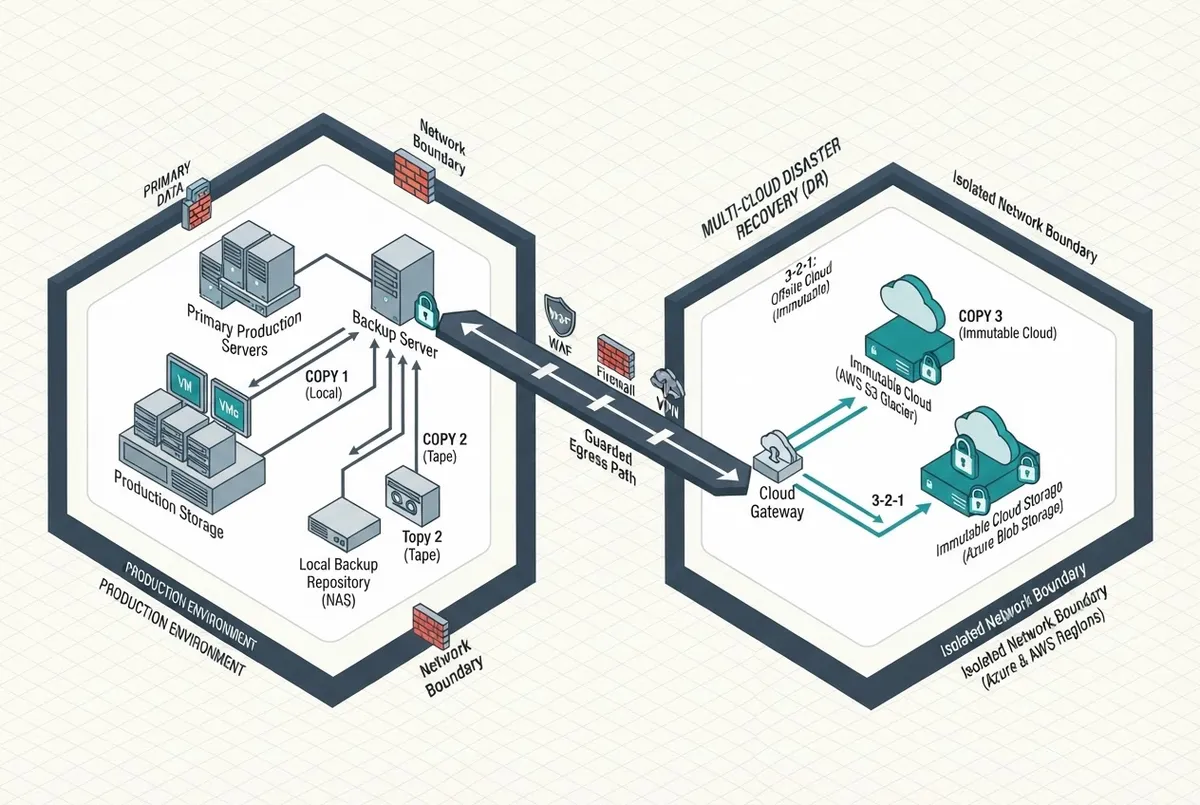
[OPS-044] · OCT 29, 2026 · STORAGE INFRASTRUCTURE
Deconstructing 3-2-1 Backups in Multi-Cloud Topologies
The traditional rule assumes independent failure domains that shared regional transit routing quietly breaks. We examine how cross-provider egress throttling impacts recovery time objectives during mass restores.
OUR EDITORIAL STANCE
Uncompromisingly Independent
Restore Point is an independent technical journal and disaster recovery proving ground. We maintain zero financial affiliations, zero referral incentives, and zero sponsored arrangements with software vendors or cloud platforms.
Our engineering runbooks and stress-test datasets are built for systems administrators and business owners who cannot afford biased tooling advice. Every snapshot evaluation, restore drill, and ransomware simulation is conducted in our privately funded bare-metal lab under uniform test parameters.
- 100% Privately Funded Bare-Metal Hardware Infrastructure
- Zero Affiliate Kickbacks, Commission Links, or Paid Reviews
- All Failure Scenarios Documented Verbatim Without Vendor Embargoes
SEAL OF EDITORIAL INTEGRITY
Protocol RP-IND-2026: Strict Non-Affiliation
Section 4.1 of the publication charter mandates that all test hardware is bought through regular retail channels at full market price. Staff engineers are strictly prohibited from holding vendor advisory roles or stock options.
INTAKE_CHANNEL // DISPATCH PROTOCOL v2.4
Submit a Tip
Send confidential disclosures, zero-day infrastructure vulnerabilities, or critical recovery documentation directly to our research desk.
PROTOCOL // GUIDELINES
Editorial Submission Rules
All submissions to Restore Point undergo cryptographic integrity checks and technical reproduction prior to publication.
- Zero telemetry retention on source IP headers
- Reproducible proof-of-concept required for CVE disclosures
- Vendor PR releases are automatically discarded
pub   ed25519/0xDE14558F 2026-01-15
Key:  4E92 B01F 8C73 2DA8 9901
      02C3 DE14 558F B270 31A9
uid:  [email protected]
[ SYS // RESTORE POINT - INDEPENDENT TECHNICAL ENGINEERING JOURNAL ]
Autonomous disaster recovery architecture, zero-trust validation matrices, and verified infrastructure playbooks for systems engineers.


INDEPENDENCE DISCLOSURE : Restore Point maintains an uncompromising operational charter. We do not accept paid placements, vendor subsidies, hardware compensation, or sponsored benchmarking drills. Architectural post-mortems and recovery assessments are conducted strictly under laboratory isolation without commercial influence.
© 2026 Restore Point. All technical documentation, benchmarks, and disaster playbooks published under Editorial Open Attribution. No proprietary commercial endorsements.